Git fixes six security flaws: update to 2.56.1
Git 2.56.1 and six backported releases fix six vulnerabilities, including one that lets a crafted repository run code when you clone it. Update Git on every machine and pipeline you build with.

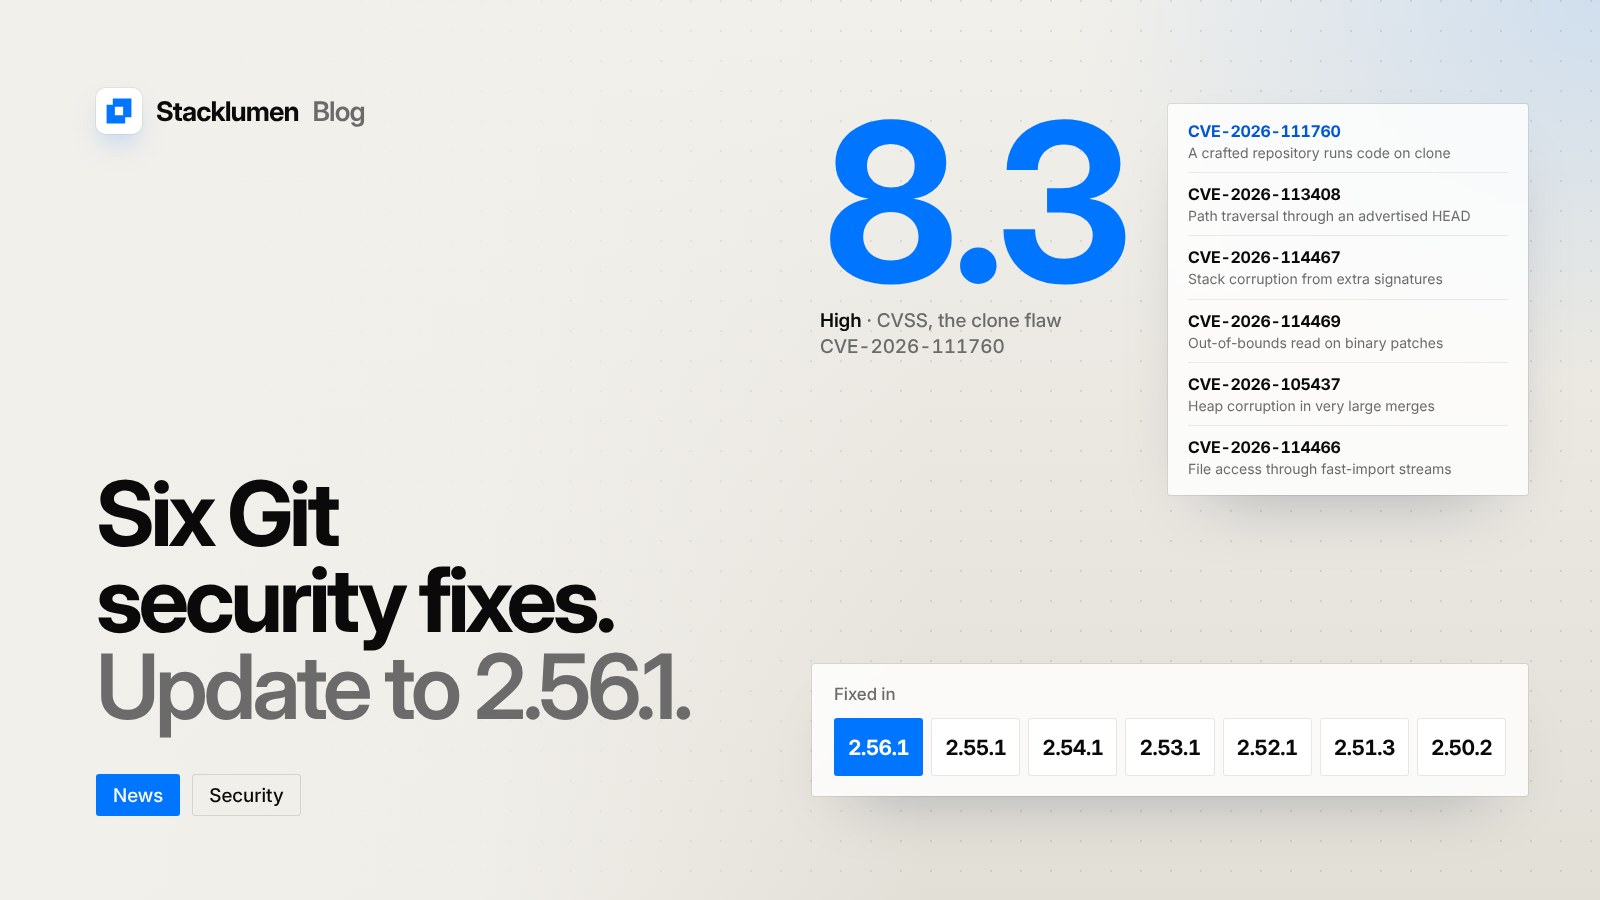
The Git project released security fixes on 10 November 2026. Git 2.56.1 fixes six vulnerabilities, and the same fixes are backported to 2.55.1, 2.54.1, 2.53.1, 2.52.1, 2.51.3 and 2.50.2. The most serious one lets a crafted repository run code on your machine when you clone it.
Git sits under almost every modern website workflow: your laptop, your build server, your deploy pipeline and any tool that pulls code for you. If any of those run an older Git, this update is worth doing this week.
The clone flaw
CVE-2026-111760 is rated High, with a CVSS score of 8.3, in the project's advisory. The release notes say an attacker-controlled repository can be crafted so that Git overwrites a gitfile, the small file Git uses for submodules, with a symbolic link to a directory holding malicious config or hooks. Those hooks can contain the attacker's own code.
GitHub's write-up adds that recursive clones can run the attacker's code during the clone itself. A plain clone can run it if you follow Git's suggestion to run git status afterwards. The fix rejects extremely long index entry paths before their length can be truncated.
The advisory lists every version up to 2.50.1, and 2.51.0 to 2.56.0, as affected.
The other five
- CVE-2026-113408. A server can advertise an unborn HEAD that contains path-traversal characters. With the files ref backend, later ref updates can write to files they should not touch.
- CVE-2026-114467. When Git strips GPG signatures from a commit message, it only allows for two. A message with more causes stack memory corruption. The release notes say this can be triggered by merging a tag with more than two signatures, which makes a denial-of-service attack possible, including on hosting services that merge for their users.
- CVE-2026-114469. Git refuses patches larger than about 1 GiB, but only checked the size of the patch as written. A small compressed binary patch that inflates past that limit could crash Git with an out-of-bounds read.
- CVE-2026-105437. In very large merges, for example many conflicts with a large
conflict-marker-size, the size of the merge buffer can overflow. Git then writes past the buffer and corrupts the heap. - CVE-2026-114466. Three
git fast-importfeatures,rewrite-submodules-to,rewrite-submodules-fromandexport-pack-edges, could read from or write to arbitrary paths. They are now disallowed by default in untrusted streams.
Who has already updated
GitHub says the fixes are deployed on github.com and its hosted enterprise service, and that patched Git is coming to GitHub Desktop, Codespaces and GitHub Actions. GitHub Enterprise Server fixes are in 3.19.16, 3.20.12, 3.21.10 and 3.22.5. A hosted service being patched does not update the Git on your own machines or servers.
What it means for your site
- Update Git everywhere you build. Check with
git --versionon your own computer, every build or deploy server, and any container image your pipeline uses. You want 2.56.1, or the patched release on your branch: 2.55.1, 2.54.1, 2.53.1, 2.52.1, 2.51.3 or 2.50.2. - Update apps that bundle Git. Desktop Git clients, code editors and CI runners often ship their own copy, so updating the system Git is not always enough.
- Be careful with unknown repositories. Until everything is patched, clone only from servers you trust, avoid recursive clones of repositories you have not reviewed, and do not merge tags or apply binary patches from sources you do not trust. GitHub notes these steps reduce risk but do not replace the update.
- Rebuild base images. If your deploy images install Git, rebuild them so new builds pick up the fixed version.
On Stacklumen, a Code site is changed on your own computer and pushed with your own git, so the Git to update is the one on your machine and in any pipeline you run.
Sources
- Git v2.50.2 release notes, describing all six fixes (Git project)
- Git v2.56.1 release notes (Git project)
- Advisory: Cloning malicious repositories can lead to arbitrary code execution (Git project)
- Git security vulnerabilities announced (GitHub blog)
- Git 2.56.1 source release, dated 10 November 2026 (kernel.org)
- Stacklumen only reads your repository (Stacklumen changelog)