PHP 8.6 is out, and 8.2 to 8.5 get security fixes
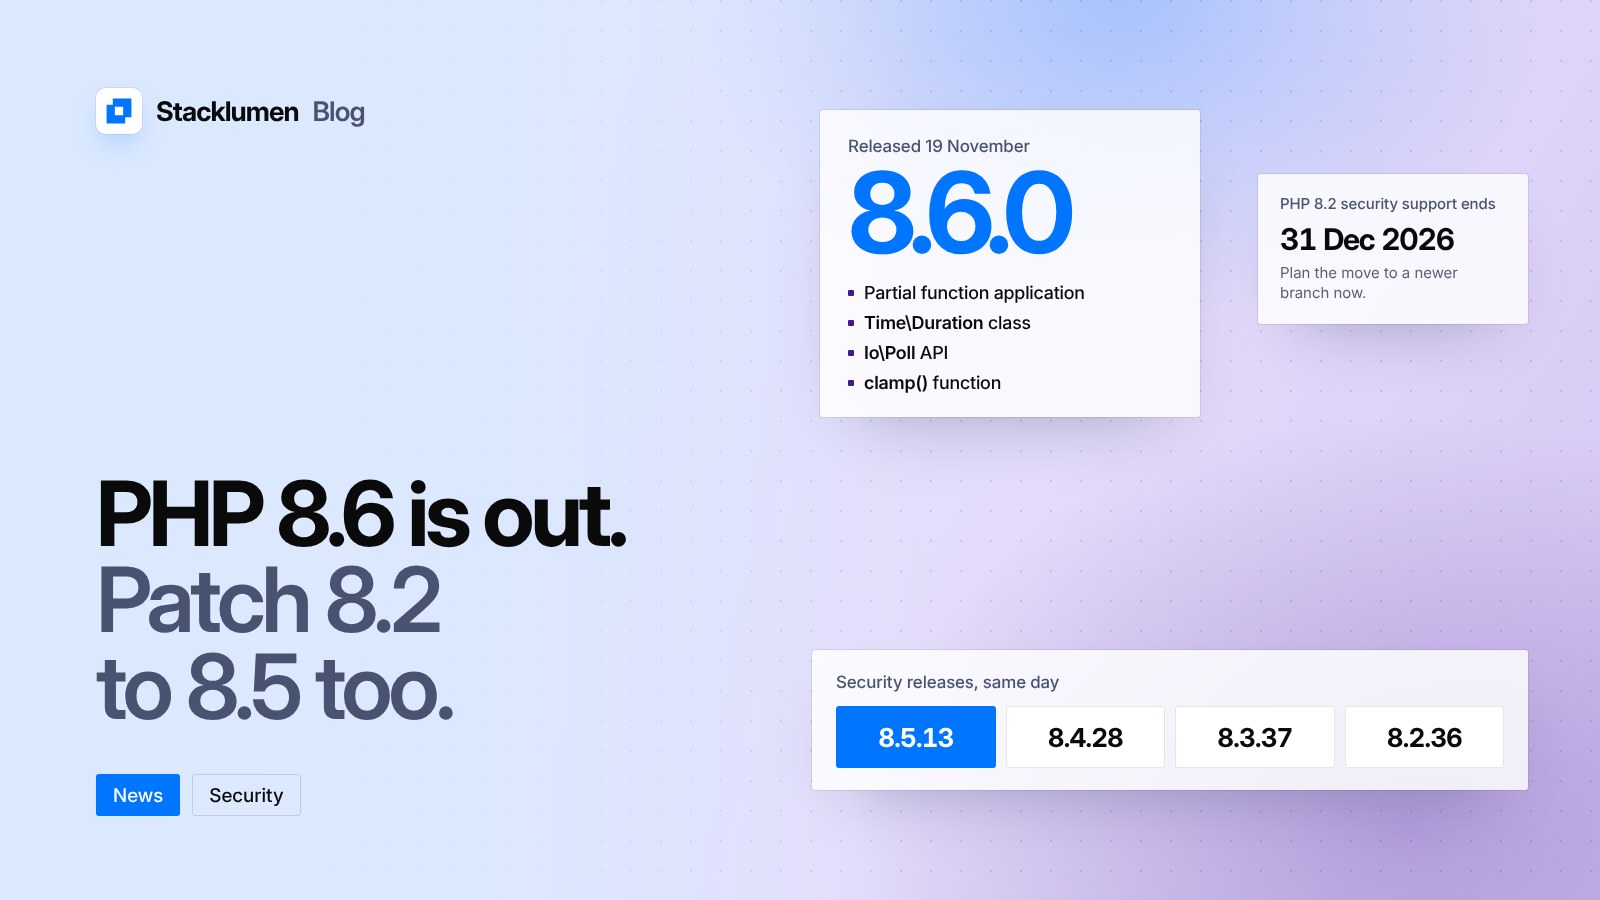
PHP 8.6.0 arrived on 19 November alongside security releases for every supported branch, with the highest-rated issues marked critical. Update to 8.5.13, 8.4.28, 8.3.37 or 8.2.36, and plan the move off PHP 8.2 before its support ends on 31 December.

On this page
PHP had a busy Thursday. On 19 November 2026 the PHP team released PHP 8.6.0, the next major version of the language, and on the same day shipped security releases for every supported branch: 8.5.13, 8.4.28, 8.3.37 and 8.2.36. If your site or a client's site runs on PHP, the security releases are the part to act on first.
The security releases
A day earlier, the PHP security team gave notice of the releases and said the highest severity among the fixed issues is critical. It also said the critical issues "require either non-default configuration or uncommon setups". Each release announcement says it is a security release and encourages everyone on that branch to upgrade.
The changelog for 8.5.13 lists the security fixes with their advisory and CVE numbers. They include:
- Session handling: partially overwritten session files, and a session serializer mismatch, each of which can lead to remote code execution (CVE-2026-126714 and CVE-2026-115560).
- PHP-FPM: request smuggling through an unread HTTP request body (CVE-2026-129289), a use-after-free that can lead to local privilege escalation (CVE-2026-129291), and cross-site scripting on the FPM status page (CVE-2026-129292).
- The engine: a use-after-free in magic method backtraces that can lead to remote code execution (CVE-2026-129474).
- PHP-CGI: an out-of-bounds read and write while correcting PATH_INFO (CVE-2026-129538).
- Other areas: the timezone cache, DOM XML serialization, SOAP, Phar signature checks and URL handling, where mixed-case HTTPS and FTPS addresses could expose data in plaintext (CVE-2026-128064).
The 8.4, 8.3 and 8.2 releases have their own sections in the same changelog. Check the one for your branch.
What is new in PHP 8.6
PHP 8.6 is a feature release. The PHP team's release page lists, among others:
- Partial function application. Some of a function's arguments can be given in advance, with
?and...placeholders for the rest. The result is a closure that runs once the remaining arguments are passed. - A
Time\Durationclass for elapsed time, independent of any time zone, with nanosecond precision. - An
Io\PollAPI for watching many streams at once, designed as a base for event loop libraries. - Stream error handling that can throw a
StreamExceptioninstead of emitting warnings. - A
clamp()function, aSortDirectionenum, default values for readonly properties, and DocComments on function parameters.
The release page also notes performance work, including faster printf() calls and faster JSON encoding. It gives no benchmark figures.
Changes to check before you upgrade to 8.6
The release page lists deprecations and behaviour changes that can affect existing code. Some that matter for websites:
- Session defaults change:
session.use_strict_modeandsession.cookie_httponlyare on, andsession.cookie_samesiteis set toLax. If your site relies on session cookies being sent on cross-site requests, test this. trim(),ltrim()andrtrim()now also strip form feed characters by default.fclose(),file_put_contents()andcopy()now returnfalsewhen flushing or closing a stream fails.- Many functions now throw a
ValueErrorfor out-of-range values, invalid flags or strings containing NUL bytes. - The mbstring regular expression functions, such as
mb_ereg(), are deprecated. The page suggests PCRE functions with theumodifier instead. - Using
returninside afinallyblock is deprecated.
The full list is in the PHP manual's migration guide for 8.6.
PHP 8.2 support ends this year
PHP's supported versions page lists security support for PHP 8.2 ending on 31 December 2026. After that date, 8.2 gets no more security fixes. PHP 8.3 has security support until 31 December 2027, 8.4 until 31 December 2028 and 8.5 until 31 December 2029.
What it means for your site
- Update now. Move to 8.5.13, 8.4.28, 8.3.37 or 8.2.36, whichever matches your branch. If a host manages PHP for you, check that it has rolled out the new builds.
- Check your setup. The PHP team says the critical issues need non-default configuration or uncommon setups. If you run PHP-FPM, PHP-CGI or custom session handling, give the changelog a careful read.
- Plan off 8.2. Sites still on 8.2 have about six weeks of security fixes left. Move them to 8.4 or 8.5, or to 8.6 once your code and dependencies support it.
- Test 8.6 before you switch. Run your site on a staging copy first, with close attention to sessions, logins and any cross-site embeds.