Rails fixes 21 security flaws: update to 8.1.4.1 or 8.0.5.2
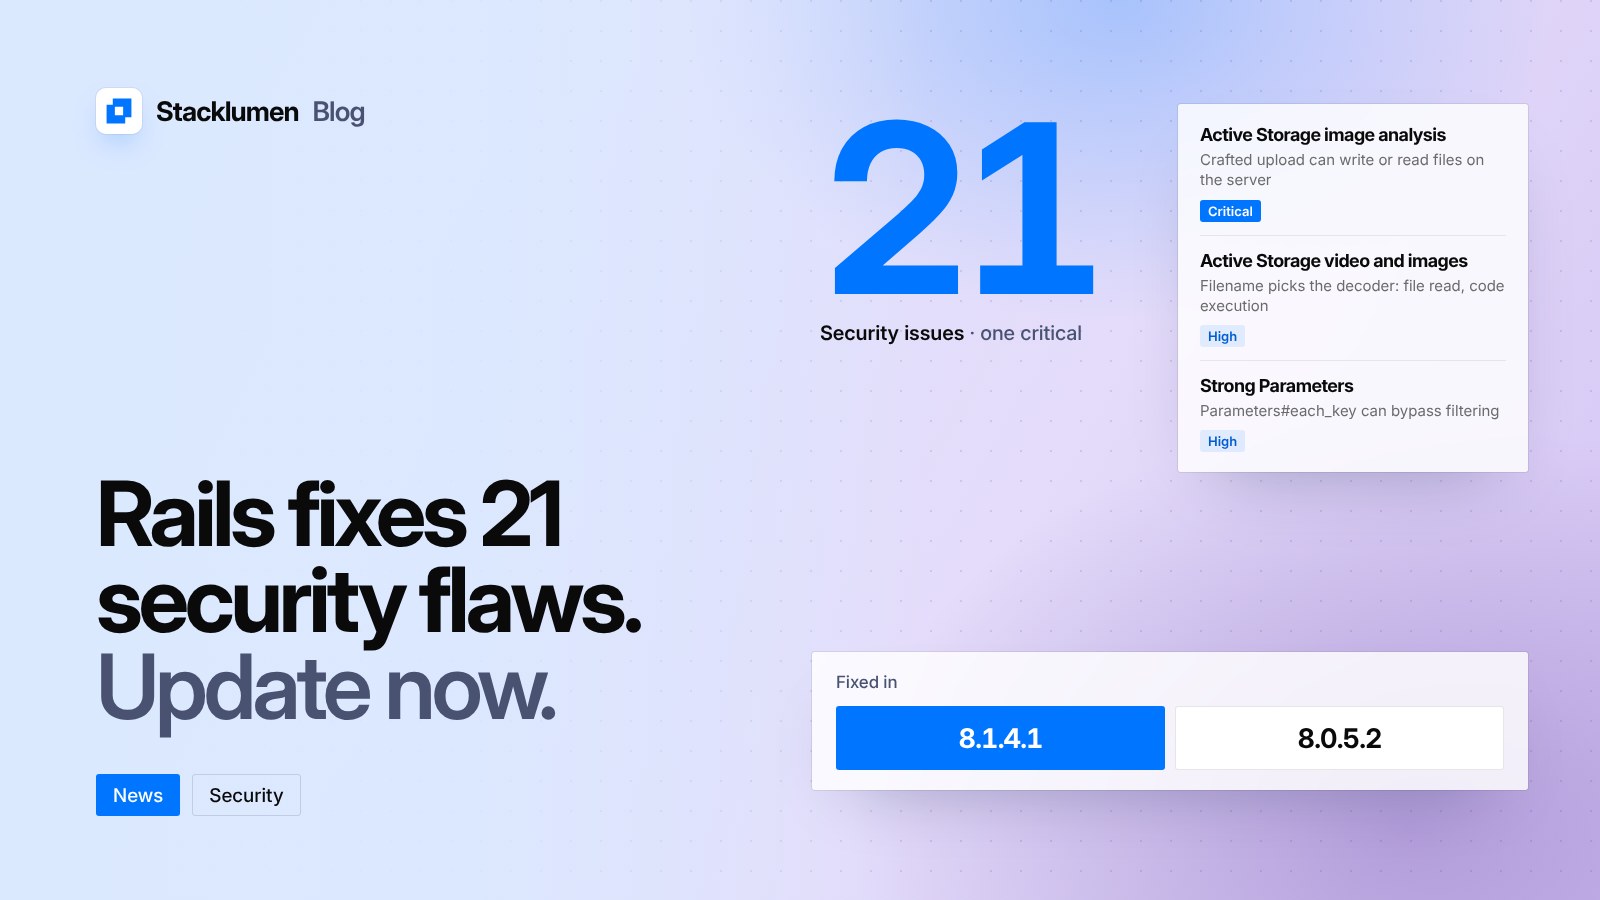
Ruby on Rails 8.1.4.1 and 8.0.5.2 fix 21 security issues, including a critical Active Storage flaw that can let an attacker write files on the server. Security support for Rails 8.0 has now ended.

On this page
Ruby on Rails released versions 8.1.4.1 and 8.0.5.2 on 4 November 2026. They fix 21 security issues across the framework. The Rails team recommends upgrading as soon as possible. One issue is rated critical, four are rated high, and most of the rest are medium.
If you run a Rails application, or look after one for a client, this is an update to schedule now.
The critical flaw: Active Storage image analysis
The most serious issue (CVE-2026-126082, GHSA-f3w6-w445-fwh9) is rated critical, with a CVSS score of 9.8. It is in Active Storage, the part of Rails that handles file uploads.
According to the advisory, an unauthenticated attacker may be able to write arbitrary files on the server. If attachments are stored with the Disk service, they may also be able to read any file the application can read, such as secret_key_base and credentials for other systems. The advisory says this could lead to remote code execution.
An application is affected if all of these are true:
- It processes images with ImageMagick through MiniMagick (
config.active_storage.variant_processor = :mini_magick). This is the default for apps usingload_defaults 6.1or earlier. - ImageMagick runs under a policy that does not deny the coders involved. The advisory says the default Debian and Ubuntu policies do not.
- It accepts file uploads from untrusted users.
Attaching a crafted file is enough. No variant, preview or analysis call is needed.
The high severity issues
Four more issues are rated high:
- Active Storage video previews, analysis and image processing (CVE-2026-126186, GHSA-v924-7rp8-4mxh, CVSS 8.8). Rails passed temporary files to ffprobe, ffmpeg and ImageMagick with the uploaded file's extension, which lets an attacker choose the decoder. The advisory describes file reads and possible remote code execution. The AviSynth route needs an FFmpeg build with AviSynth enabled, which standard upstream, Linux distribution and Homebrew builds do not have.
- Action Pack
Parameters#each_key: a bypass of Strong Parameters (GHSA-wm3x-v3qw-4jh3). - Action Dispatch
RemoteIp: IP address spoofing through theForwardedheader, in 8.1 only (GHSA-2gff-2mmg-m73p). - Active Support
safe_constantize: denial of service (GHSA-8474-xrp6-wh69).
Everything else
The medium and low issues include four cross-site scripting flaws in Action View helpers (text helpers, highlight, strip_tags and tag helpers), several denial of service issues, cache poisoning through content negotiation, destroyed sessions being restored in CacheStore, and session cookies missing a SameSite attribute. Each advisory is linked from the release post, with patches for teams that cannot upgrade straight away.
Rails 8.0 support has ended
The release post also notes that security support for the Rails 8.0 series ended on 7 November 2026. Version 8.0.5.2 fixes these issues, but future security fixes will not come to 8.0. Apps on 8.0 should plan a move to 8.1.
What it means for your site
- Upgrade. Move Rails 8.1 apps to 8.1.4.1 and Rails 8.0 apps to 8.0.5.2, then deploy.
- Check your image setup. If your app uses MiniMagick and accepts uploads, the critical flaw applies. The advisory lists mitigations if you cannot upgrade yet: use mini_magick 5.1 or later, and copy the policy rules Rails ships into ImageMagick's system policy, denying at least the MSL coder, the Ghostscript coders and the
gsdelegate. - Rotate secrets if you were exposed. If your app was affected and stores files with the Disk service, the advisory recommends rotating
secret_key_baseand every secret the process can read, including the master key, credentials, storage and database credentials, and third-party tokens. - Video uploads. If you cannot upgrade, the high severity advisory suggests removing the video previewer and the video and audio analyzers from your Active Storage configuration until you can.
- Plan the 8.0 move. If a client site still runs on Rails 8.0, put the upgrade to 8.1 on the schedule.